

Project roles
When a user is assigned to a project, they must also be assigned a project role.
Create a new project role
Navigate to Engineering -> Roles
Configure project role
The following settings can be made via the project role options
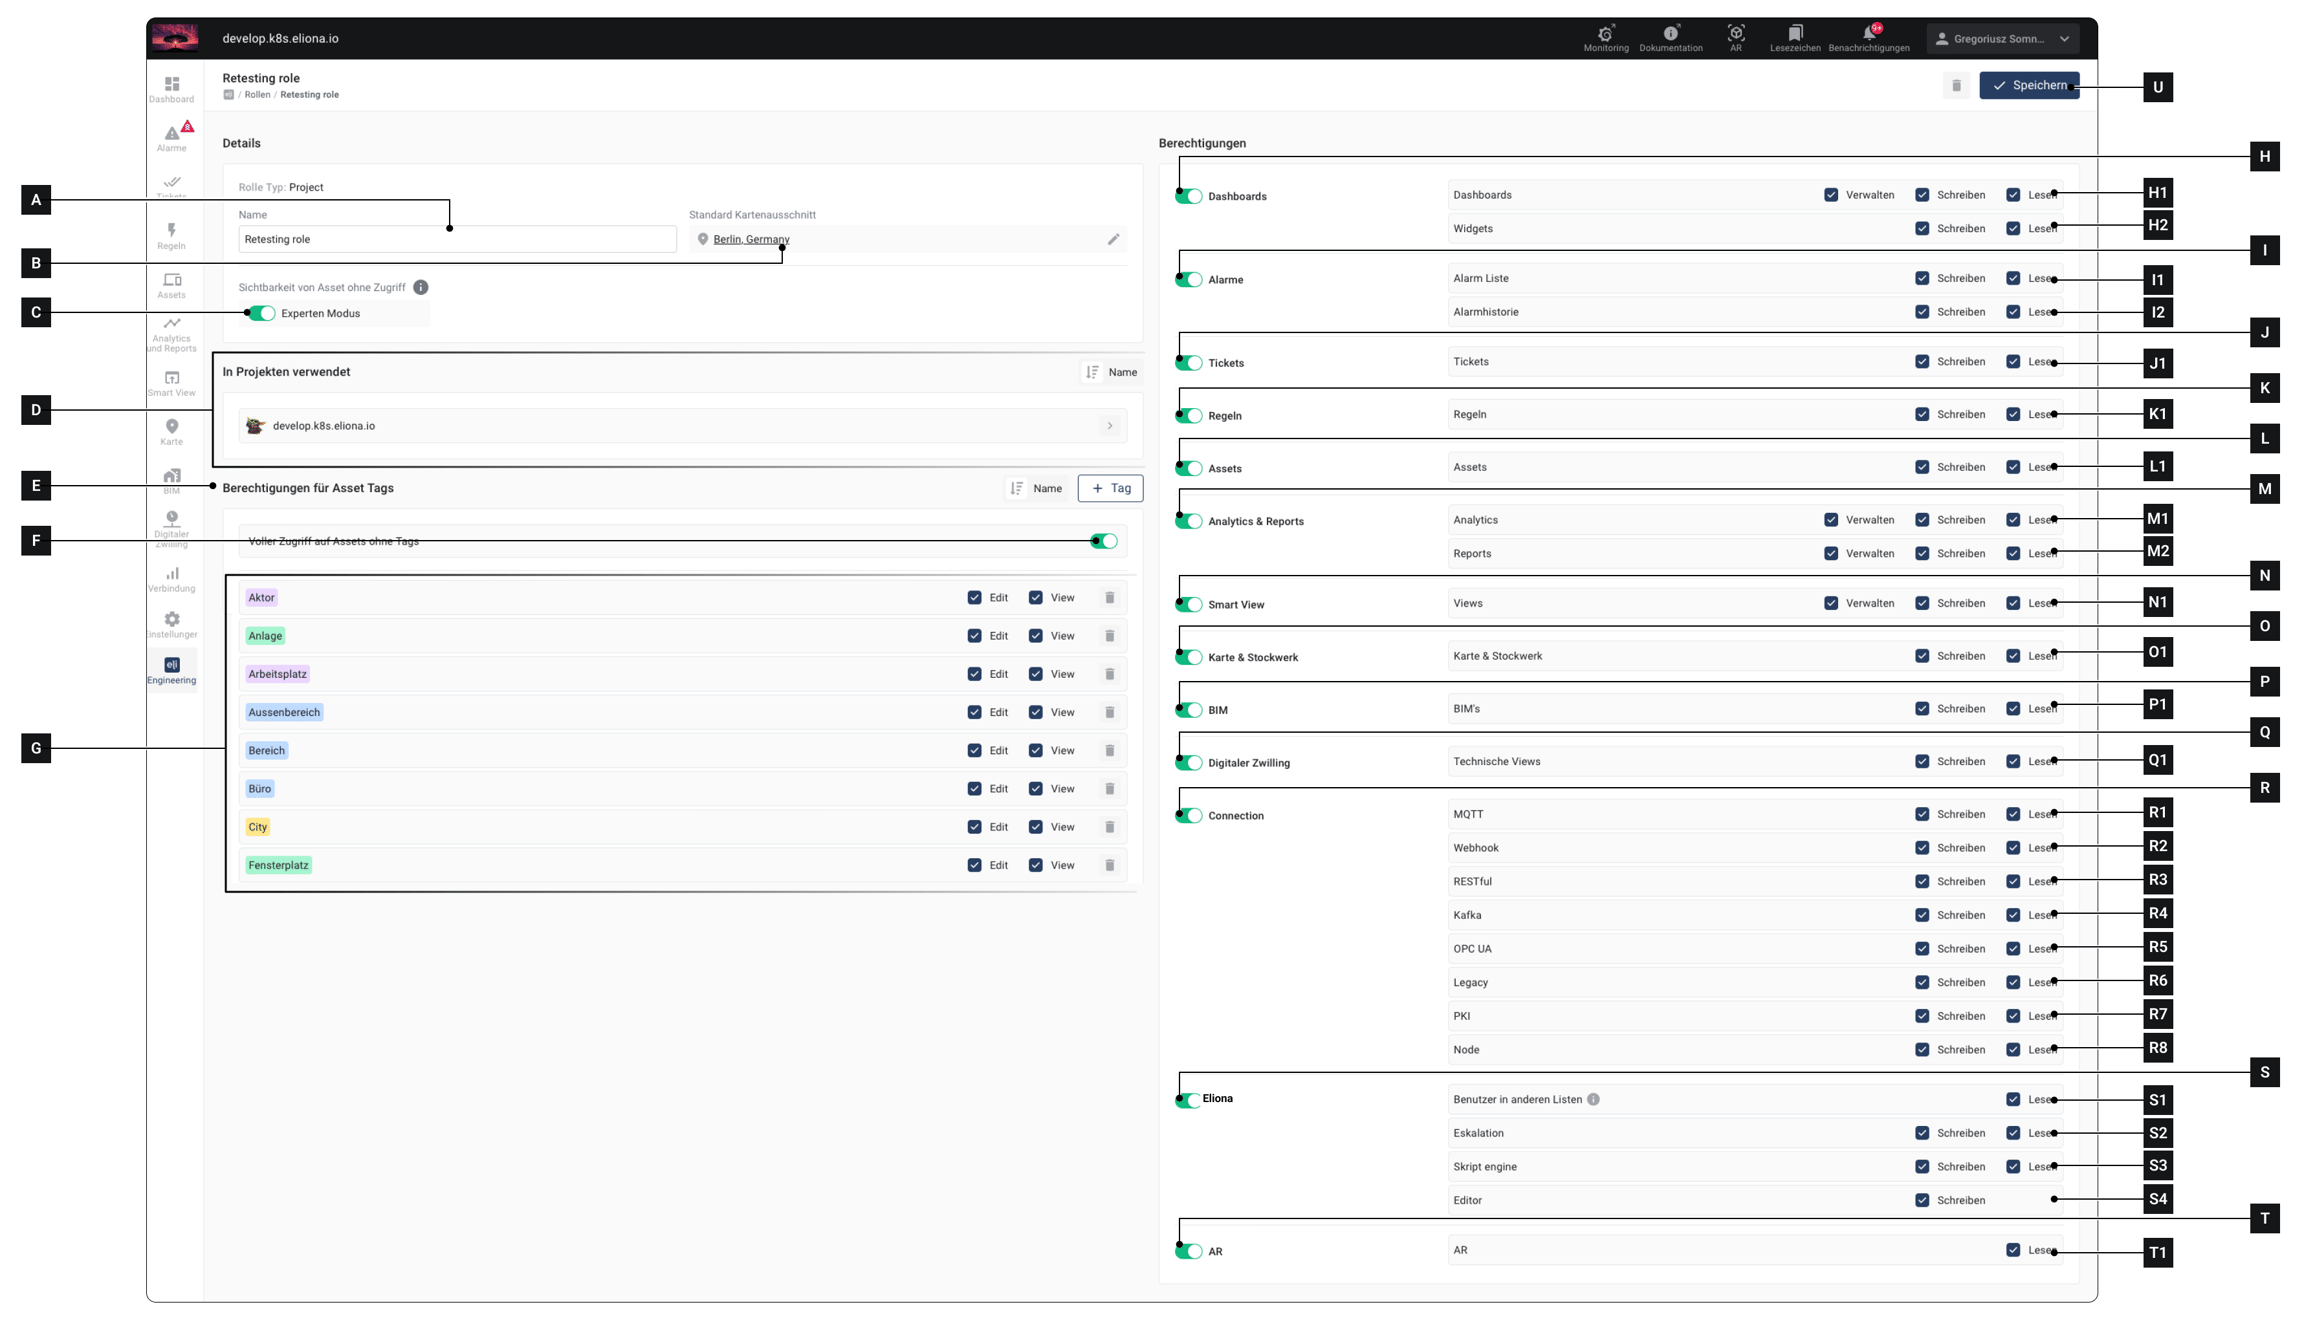
[A]
Name
Name of the project role
[D]
Used in projects
Indicates in which projects this role is used
[F]
Full access to assets without tags
If this switch is enabled, users with this role have full access to assets that are not tagged. ↗ Full access to assets without tags
[G]
Tags
A list of all tags to which holders of this role have access
[H]
Universal switch «Dashboards»
Enable/disable all write permissions and read permission for the function «Dashboards»
[H1]
Dashboards
Enable/disable write and read access for the function «Dashboards»
[H2]
Widgets
Enable/disable write and read access for the function «Widgets»
[I]
Universal switch «Alarm»
Enable/disable all write permissions and read permission for the function «Alarms»
[I1]
Alarms
Enable/disable write and read access for the function «Alarms»
[I2]
Alarm history
Enable/disable write and read access for the function «Alarm history»
[J]
Universal switch «Tickets»
Enable/disable all write permissions and read permission for the function «Tickets»
[J1]
Augmented Reality
Enable/disable write and read access for the function «Augmented Reality»
[K]
Universal switch «Rules»
Enable/disable all write permissions and read permission for the function «Rules»
[K1]
Asset Editor
Grant write permission/read permission for the «Asset Editor»
[L]
Universal switch «Assets»
Enable/disable all write permissions and read permission for the function «Assets»
[L1]
Assets
Enable/disable write and read access for the function «Assets»
[M]
Universal switch «Analytics and Reports»
Enable/disable all write permissions and read permission for the function «Analytics and Reports»
[M1]
Analytics
Enable/disable write and read access for the function «Analytics»
[M2]
Reports
Enable/disable write and read access for the function «Reports»
[N]
Universal switch «Smart View»
Enable/disable all write permissions and read permission for the function «Smart View»
[N1]
Views
Enable/disable write and read access for the function «Smart Views»
[O]
Universal switch «Map and Floor»
Enable/disable all write permissions and read permission for the function «Map and Floor»
[O1]
Map and Floor
Enable/disable write and read access for the function «Map and Floor»
[P]
Universal switch «BIM»
Enable/disable all write permissions and read permission for the function «BIM»
[P1]
BIM
Enable/disable write and read access for the function «BIM»
[Q]
Universal switch «Digital Twin»
Enable/disable all write permissions and read permission for the function «Digital Twin»
[Q1]
Digital Twin
Enable/disable write and read access for «Digital Twin»
[R]
Universal switch «Connection»
Enable/disable all write permissions and read permission for the function "Connection"
[R1]
MQTT
Enable/disable write and read access for "MQTT"
[R2]
Webhook
Enable/disable write and read access for „Webhook“
[R3]
RESTful
Enable/disable write and read access for „RESTful
[R4]
Kafka
Enable/disable write and read access for „Kafka“
[R5]
OPC UA
Enable/disable write and read access for „OPC UA“
[R6]
Legacy
Enable/disable write and read access for „Legacy
[R7]
PKI
Enable/disable write and read access for „PKI
[R8]
Node
Enable/disable write and read access for "Node"
[S]
Universal switch «Engineering»
Enable/disable all write permissions and read permission for the function "Settings"
[S1]
Users in other lists
If this function is enabled, users can under certain circumstances see the names of other users, even if they are not enabled for this in the corresponding system role. ↗ More information
[S2]
Escalation
Enable/disable write and read access for the function „Escalation“
[S3]
Script Engine
Enable/disable write and read access for the function „Script Engine“
[S4]
Asset Editor
Enable/disable write and read access for the function "Asset Editor"
[T]
Universal switch «AR»
Enable/disable all write permissions and read permission for the function "Smart Assist"
[T1]
AR
Enable/disable write permissions and read permission for the function "Smart Assist"
[U]
Save
You must save your selection
Ticket permissions
The universal switch Tickets [J] controls access to the ticket area. The ticket list view, ticket details and tasks are separately authorized. For ticket details and tasks, the levels Read, Write and Managedetermine who can view, create, edit or manage content. In addition, special rules apply to assignees and creators.
-> Permissions for tickets and tasks
[C] The Expert Mode
If Expert Mode is enabled, ↗ Entities (e.g. tickets, digital twins, etc.) can be accessed that are assigned to assets to which the role actually has no access.
Example 1
An asset is tagged with «A», «B» and «C»
The user has read permission for tag A
The user has no read permission for tag B and tag C
The option „Expert Mode“ is irrelevant in this example
▷ The user sees the asset in the asset overview
▷ The user sees tickets that relate to this asset
▷ In a ticket, the user sees the name of the asset. By clicking on the asset name, the user can open the asset details.
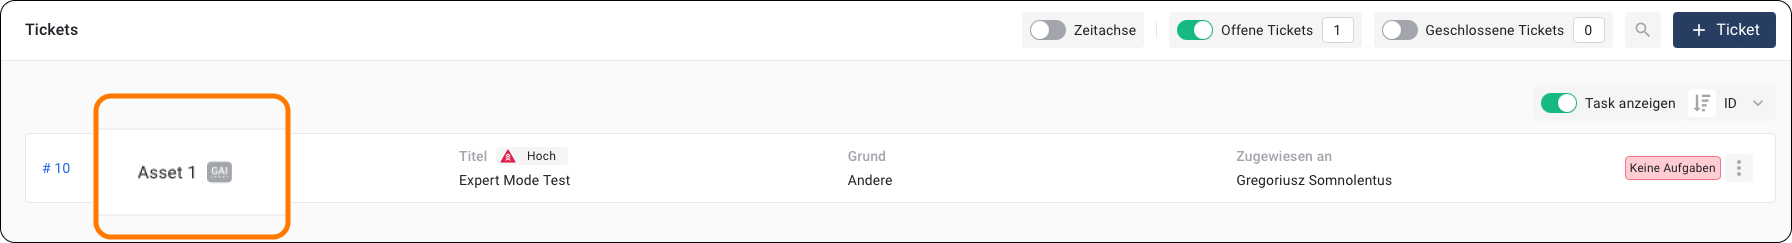
Example 2
An asset is tagged with «A», «B» and «C»
The user has no read permission for the 3 tags
The option „Expert Mode“ is not enabled
▷ The user does not see the asset in the asset overview
▷ The user does not see any tickets that relate to this asset
Example 3
An asset is tagged with «A», «B» and «C»
The user has no read permission for all tags
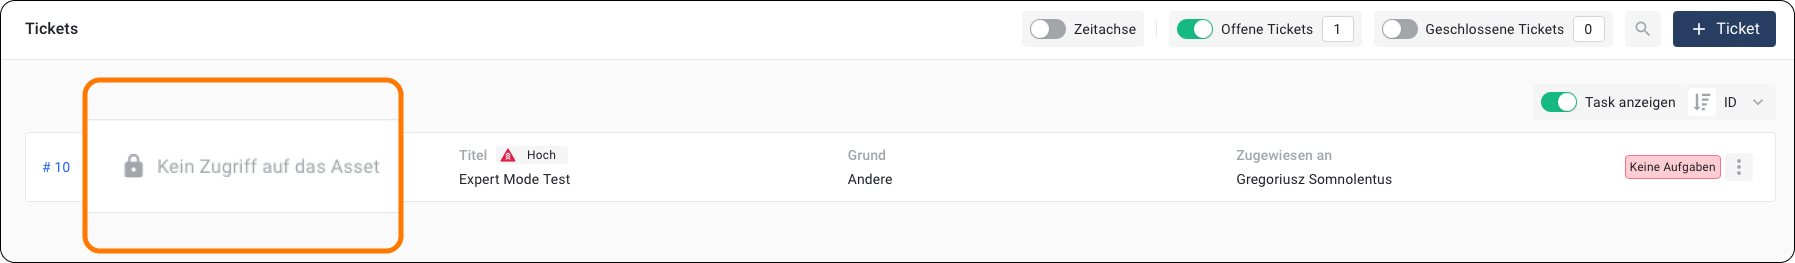
The option „Expert Mode“ is enabled
▷ The user does not see the asset in the asset overview
▷ The user sees tickets that relate to this asset
▷ In these tickets, the user does not see the name of the asset
[E] Asset Tags
If you add one or more tags here, this role can only see assets that are tagged with these tags. All other assets will be hidden.
Example: You add the tag "Ventilation systems". This role will only be able to access assets that are tagged with the tag "Ventilation systems".
[F] Full access to assets without tags
If this option is enabled: Users have full access to all assets that have no (0) tags.
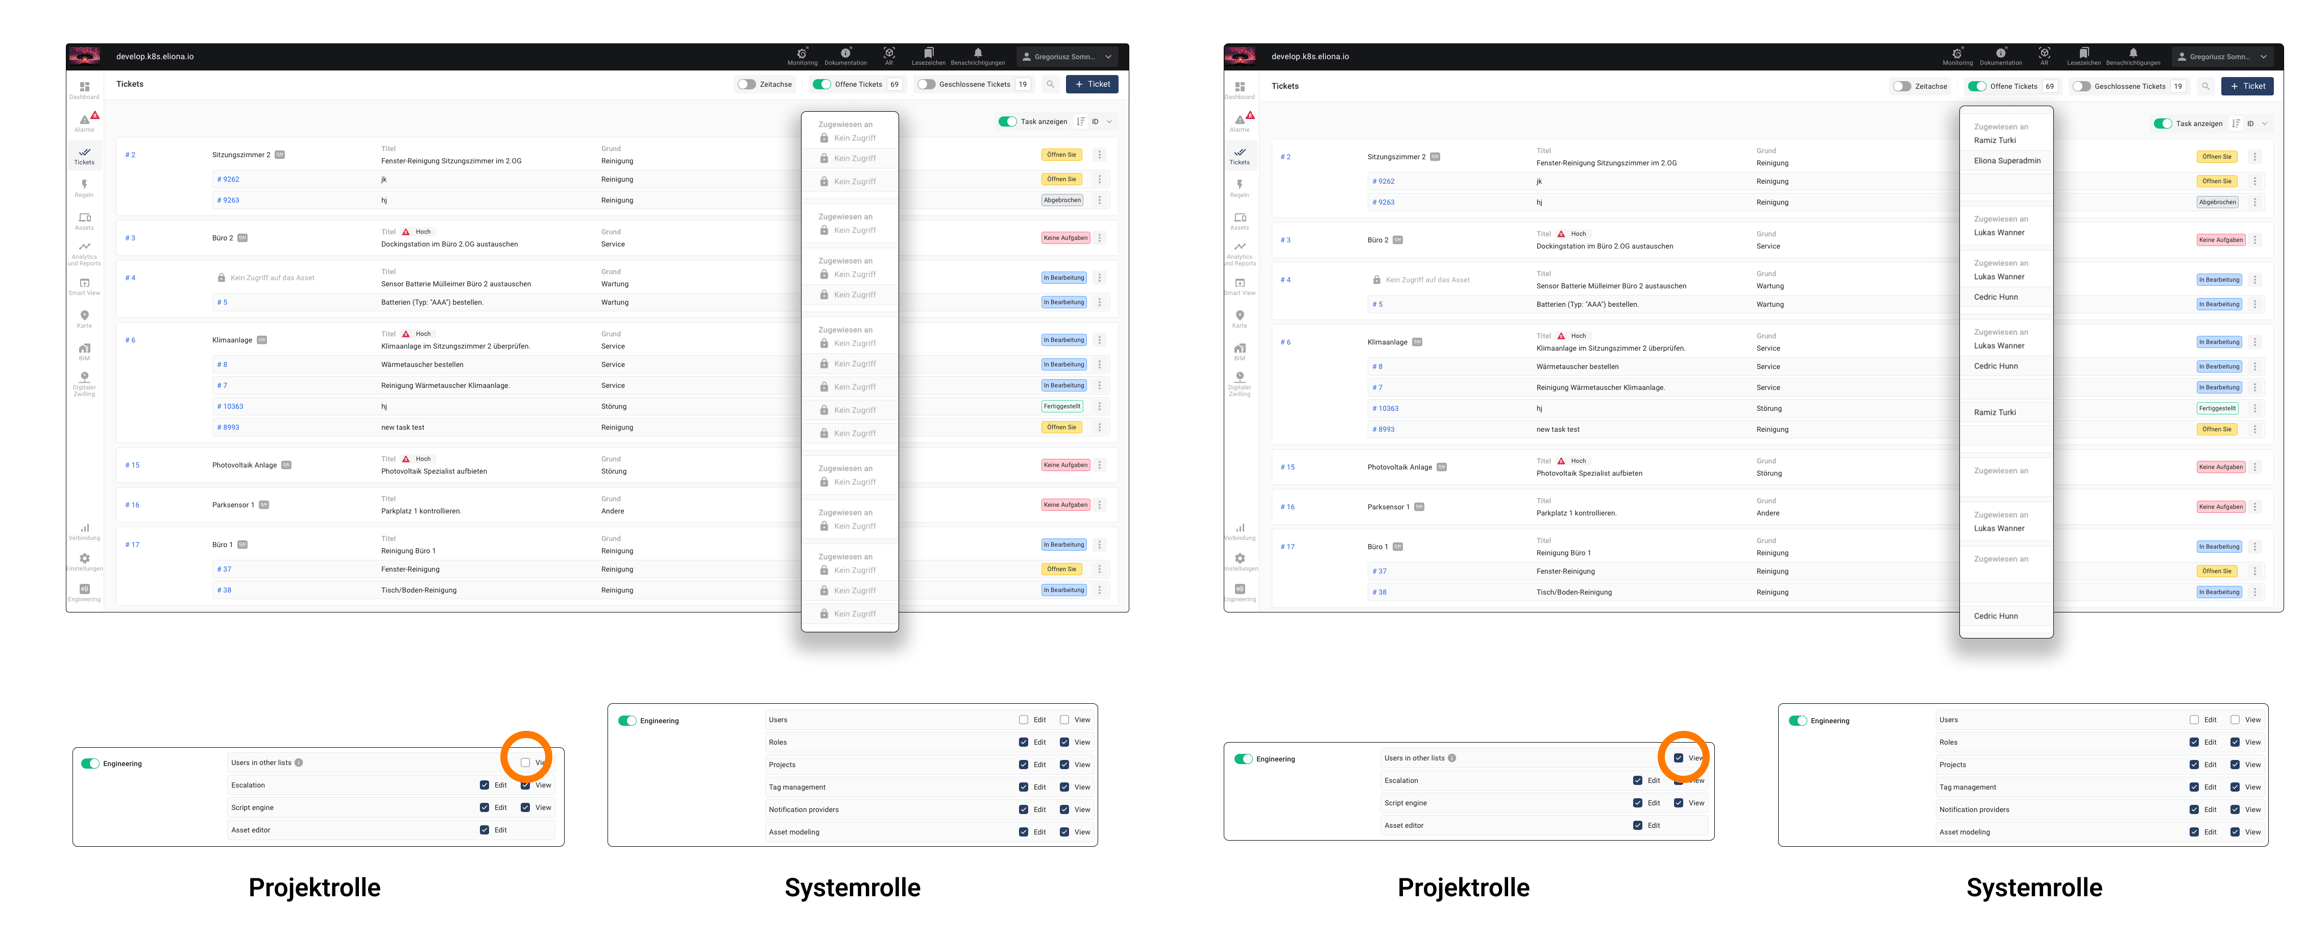
[S1] - Users in other lists
Whether a user can see the usernames of other users is actually defined in the system role. In certain cases, it may be desirable for users to be able to see the names of other users even though they lack the rights for this in the system role.
For this, the toggle [S1] can be enabled.
In the example below, a user can see the usernames after this option has been enabled.
Assign a project role to a user
Last updated
Was this helpful?